Skip to the main content.

ABT Blog

Read about mortgage technology solutions topics

Regulatory Compliance

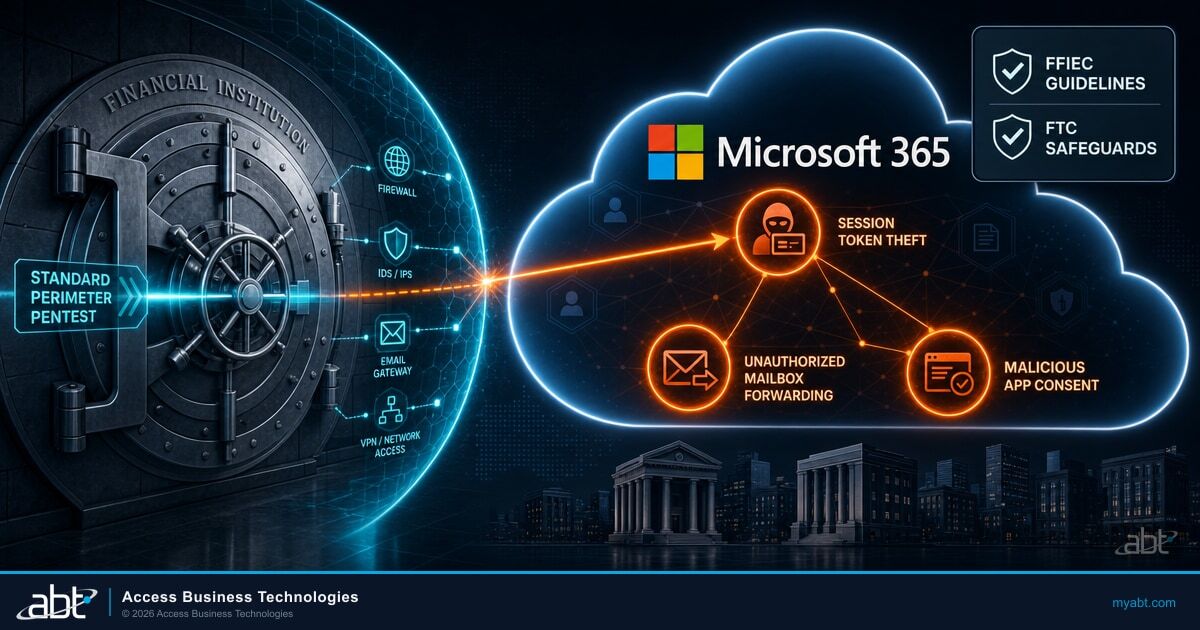
A standard perimeter penetration test stops at the network edge while session token theft, mailbox forwarding and malicious app consent happen inside the Microsoft 365 tenant

14 min read

Microsoft 365 Penetration Testing for Financial Institutions

In This Article What a penetration test is, in your regulator's words What your regulator actually requires What Microsoft permits you to test The...
Read More
Microsoft Power Pages admin panel showing Anonymous Access set to Allowed, with customer records flowing out of an open vault

11 min read

Power Pages Misconfiguration: No CVE, No Patch

Two financial regulators flagged a Microsoft Power Pages setting that exposes Dataverse records. No CVE, no patch, and your scanner will not see it.
Read More
An open manila vendor file folder on a desk holding printed audit reports, with a card bearing the Microsoft 365 logo resting on top and a tab labeled VENDOR FILE

17 min read

Vendor Due Diligence on Microsoft 365: What Goes in the File

In This Article The Questionnaire That Comes Back Empty The Passage That Answers This Step One: Document the Limitation Step Two: Obtain Alternative...

Read More
Microsoft Entra ID legacy risk policies deactivated with an October 1 2026 deadline, replaced by Conditional Access protecting bank accounts

14 min read

Entra Risk Policies Retire Oct 1, 2026: What Banks Must Do

In This Article What actually changes on October 1 The self-service loop that goes away first The detections keep firing. No risk policy acts on...
Read More
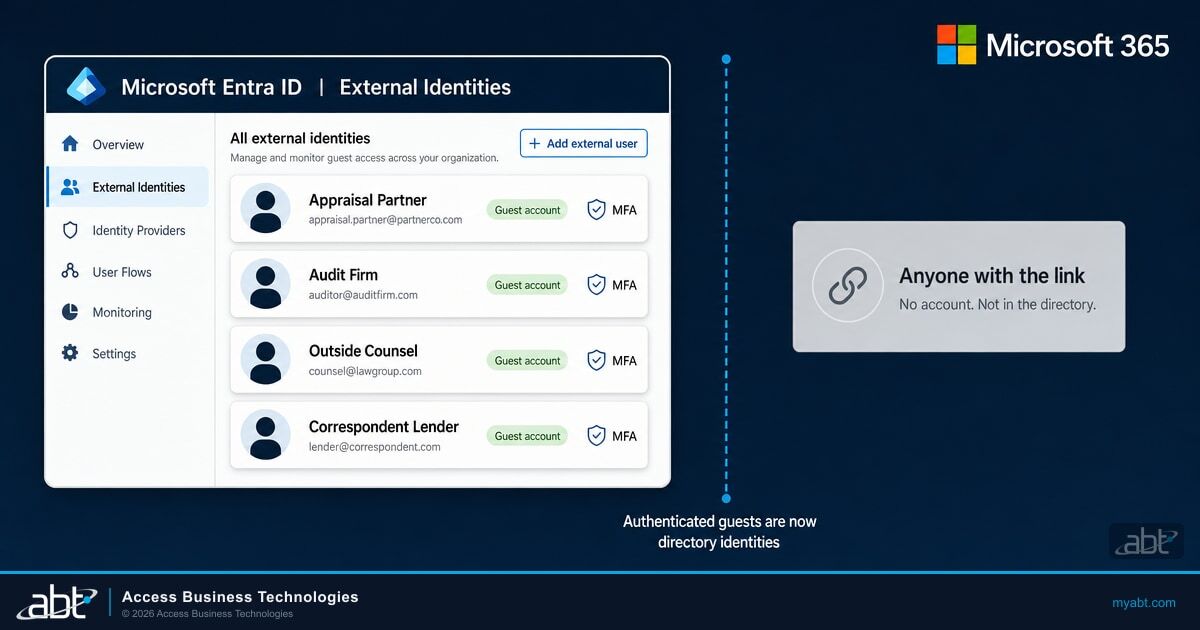
Microsoft Entra ID External Identities panel showing four external guest accounts with MFA, beside an Anyone with the link card outside the directory perimeter

14 min read

Microsoft 365 Guest Access for Financial Institutions

In This Article What changed in your tenant this summer Guest access, external access, and Anyone links are three different doors The blind spot...
Read More
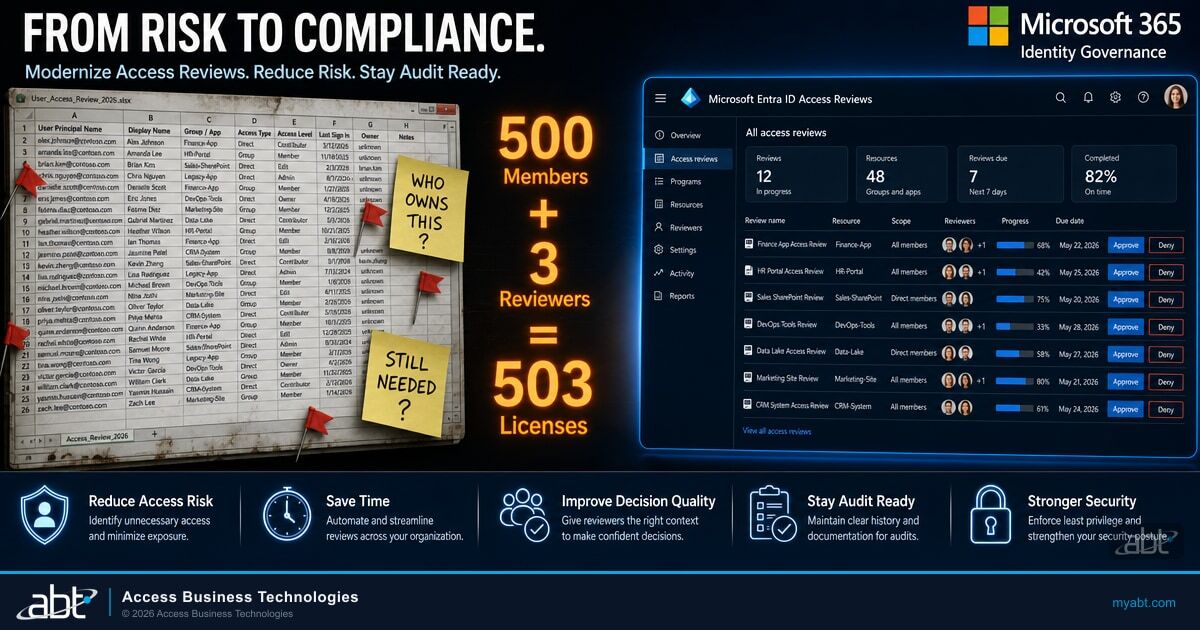
Microsoft Entra ID access reviews console replacing a manual access review spreadsheet, showing that a 500 member group reviewed by 3 owners requires 503 licenses

13 min read

Entra ID Access Reviews for Financial Institutions

Your examiner expects two layers of user access review: resource owners verifying that access matches job roles, plus a periodic independent check....
Read More
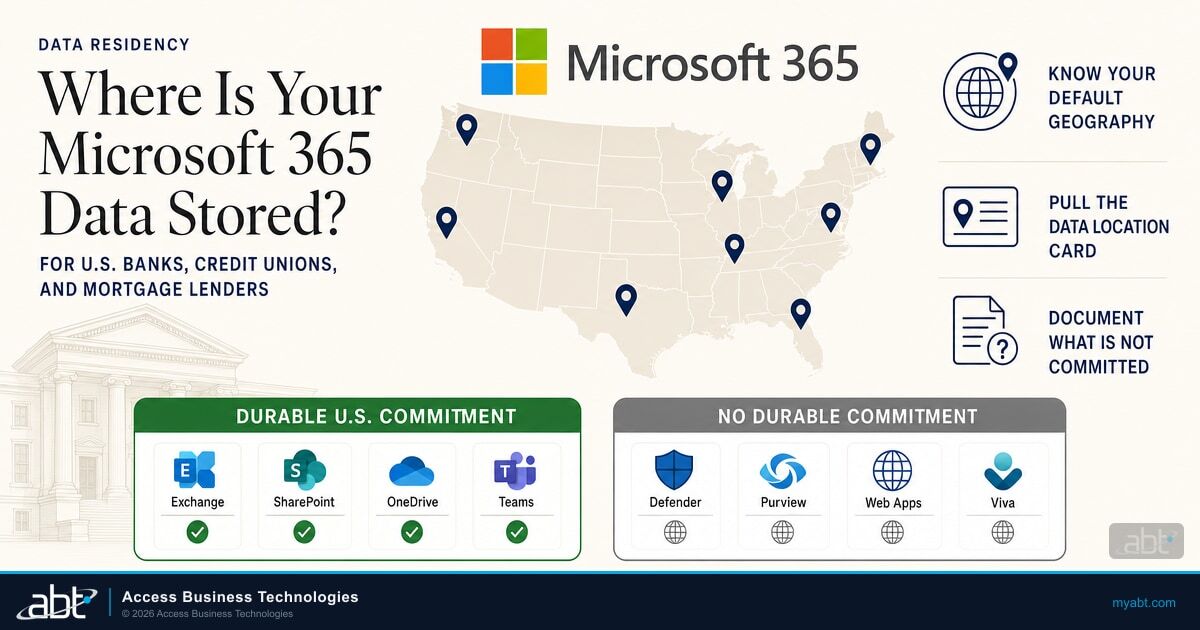
Where is your Microsoft 365 data stored, showing four services with a durable United States commitment and four without

11 min read

Where Is Your Microsoft 365 Data Stored? Data Residency for US Financial Institutions

A vendor questionnaire asks where your Microsoft 365 data is stored. For a United States tenant, four services carry a durable commitment and four do...
Read More
Cyber insurance renewal checklist mapped to a Microsoft 365 security panel showing Microsoft Entra, Microsoft Defender, and Microsoft Purview.

12 min read

Cyber Insurance Requirements Mapped to Microsoft 365 for Financial Institutions

In This Article Cyber Coverage Became a Controls Exam What Carriers Actually Require Now The Control to Microsoft 365 Map Where Microsoft 365 Falls...
Read More
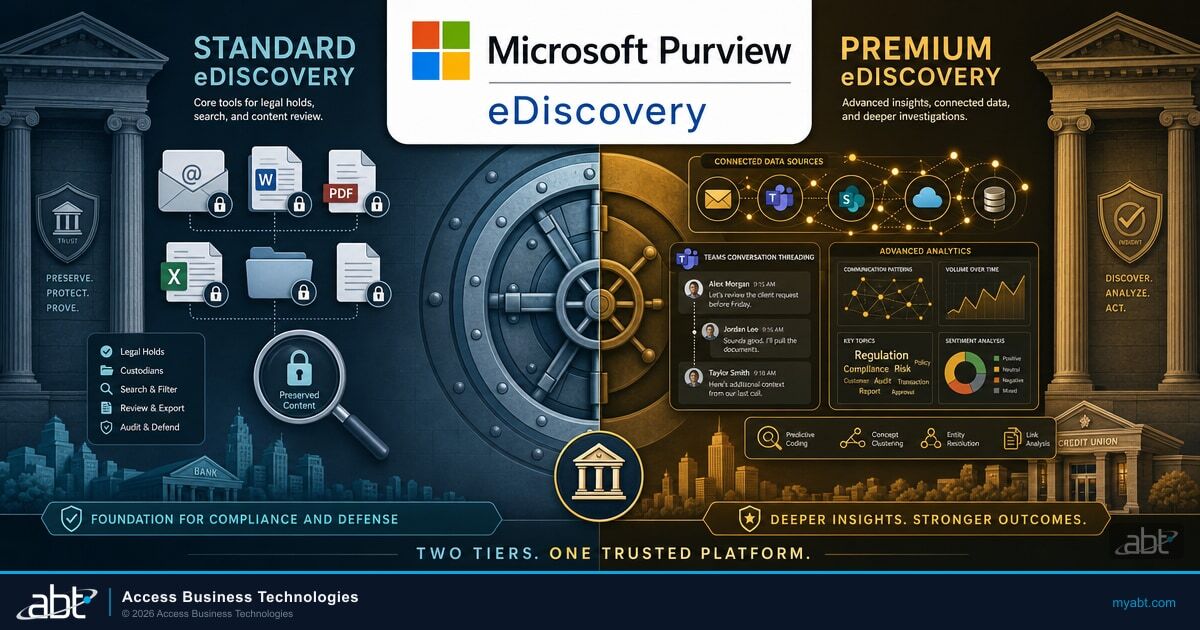
Microsoft Purview eDiscovery for financial institutions: the licensing rule that reverses between Standard and Premium tiers

16 min read

Microsoft Purview eDiscovery for Financial Institutions: The Licensing Rule That Reverses

In This Article What Purview eDiscovery Actually Does Standard Versus Premium: What Each Tier Buys The Licensing Rule That Reverses The Shared...
Read More

12 min read

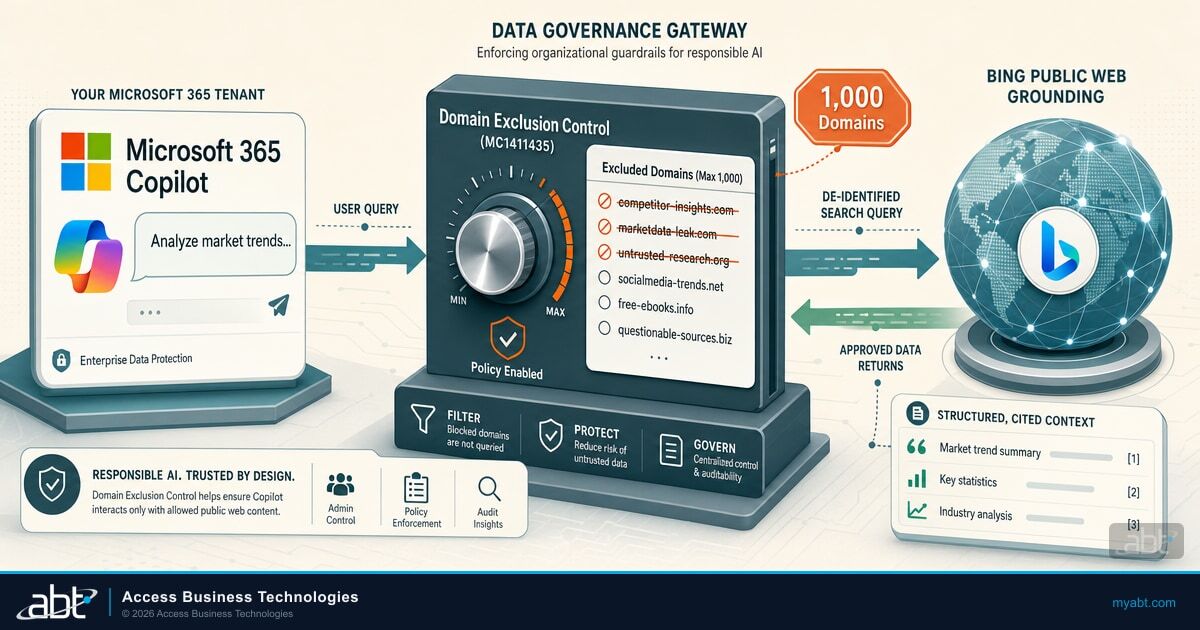
Microsoft 365 Copilot Web Grounding Domain Exclusion for Financial Institutions

In This Article What Web Grounding Actually Does in Copilot What Leaves Your Tenant, and What Does Not Domain Exclusion (MC1411435): Shipped in July,...

Read More