
10 min read
HIPAA Security Rule 2026: What the Final Rule Means for Your Risk Analysis
In This Article The Proposed Rule and the 240-Day Window Addressable Becomes Required Six Concrete Changes That Will Hit Your IT Operations The OCR...
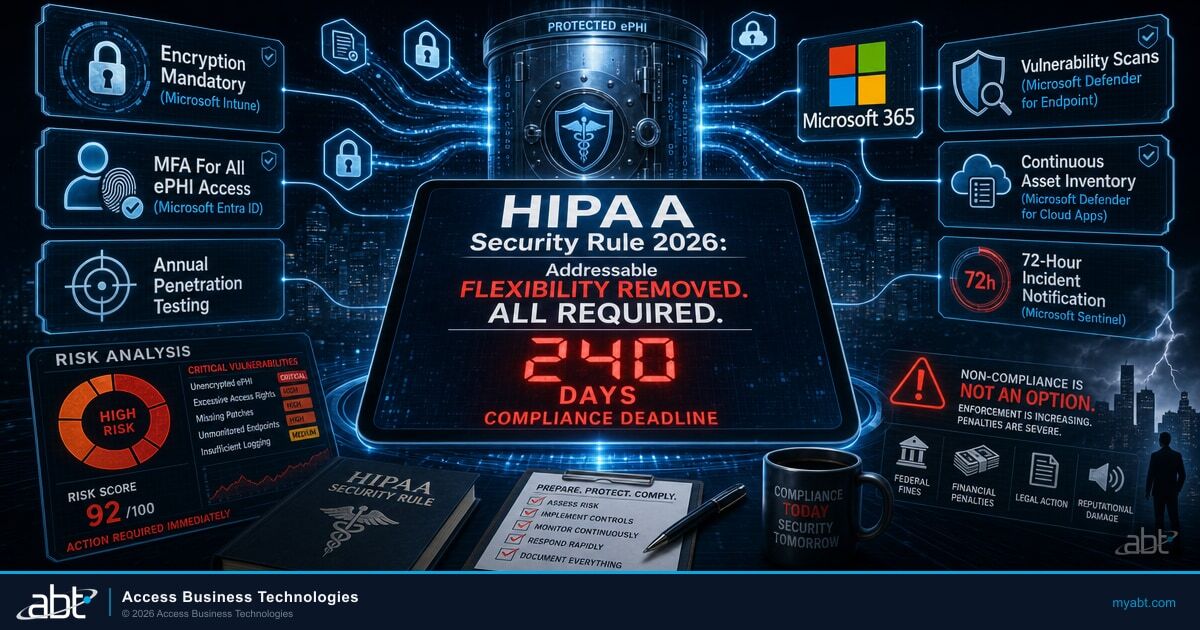
10 min read
In This Article The Proposed Rule and the 240-Day Window Addressable Becomes Required Six Concrete Changes That Will Hit Your IT Operations The OCR...
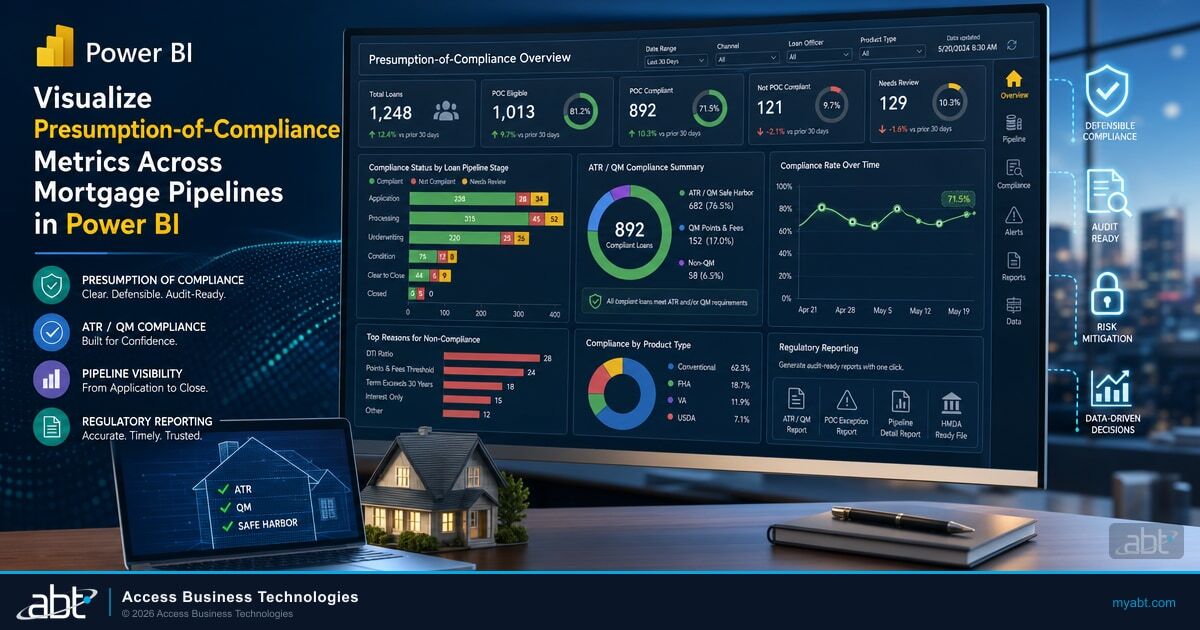
9 min read
In This Article Why QM Tracking Cannot Live in Spreadsheets Anymore What Is Presumption of Compliance? Why Power BI for Compliance Tracking Template...
13 min read
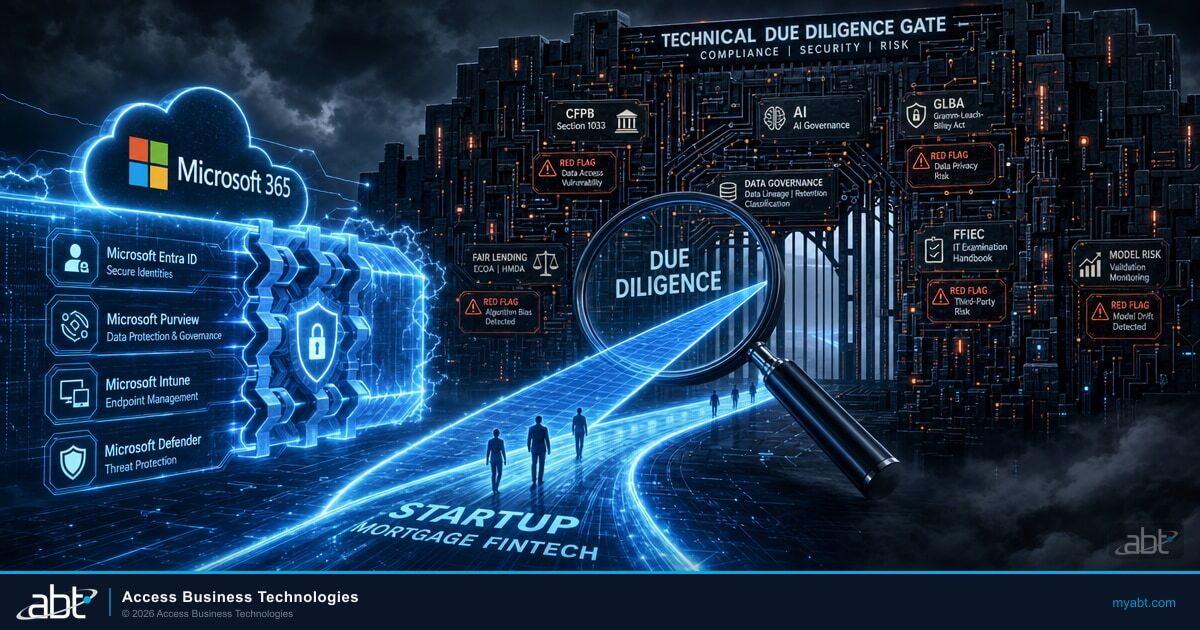
The OCC, Federal Reserve, and FDIC unified third-party risk management under a single interagency standard on June 6, 2023. Three years later,...
8 min read
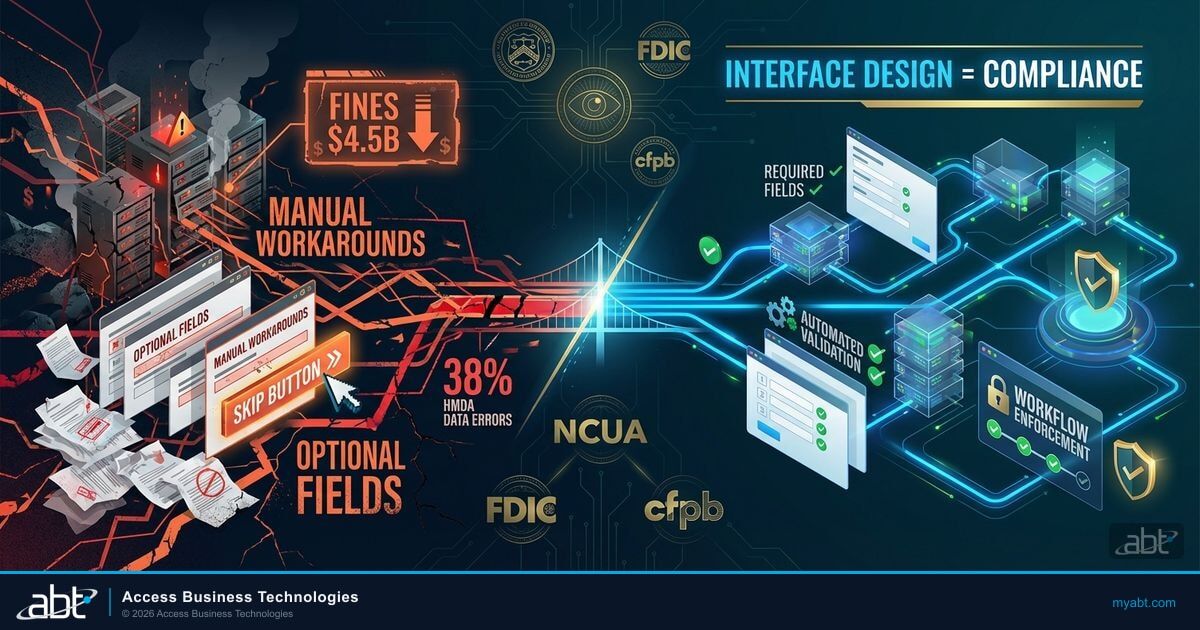
In This Article The Multi-Regulator Enforcement Landscape in 2025-2026 Five Violation Categories That Start with Bad Systems How Interface Design...
13 min read
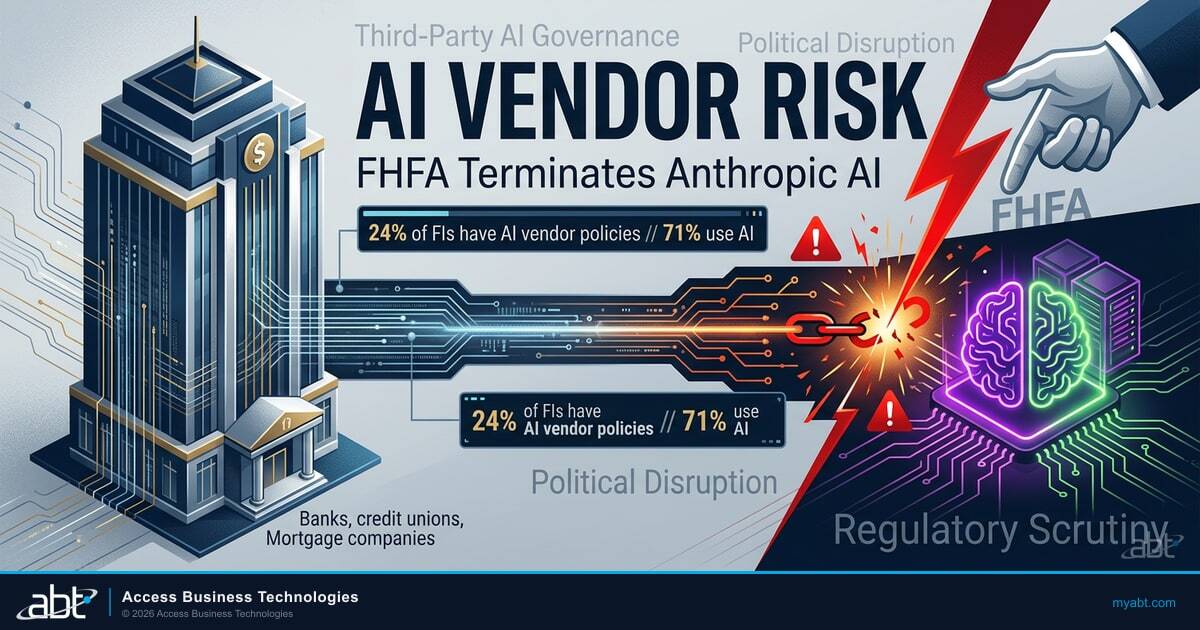
In This Article What Happened: FHFA Terminates Anthropic AI Contract Why Financial Institutions Should Pay Attention The AI Governance Gap Across...
14 min read
On December 10, 2025, OWASP released the first security framework built specifically for AI systems that can take autonomous actions. The OWASP Top...
13 min read
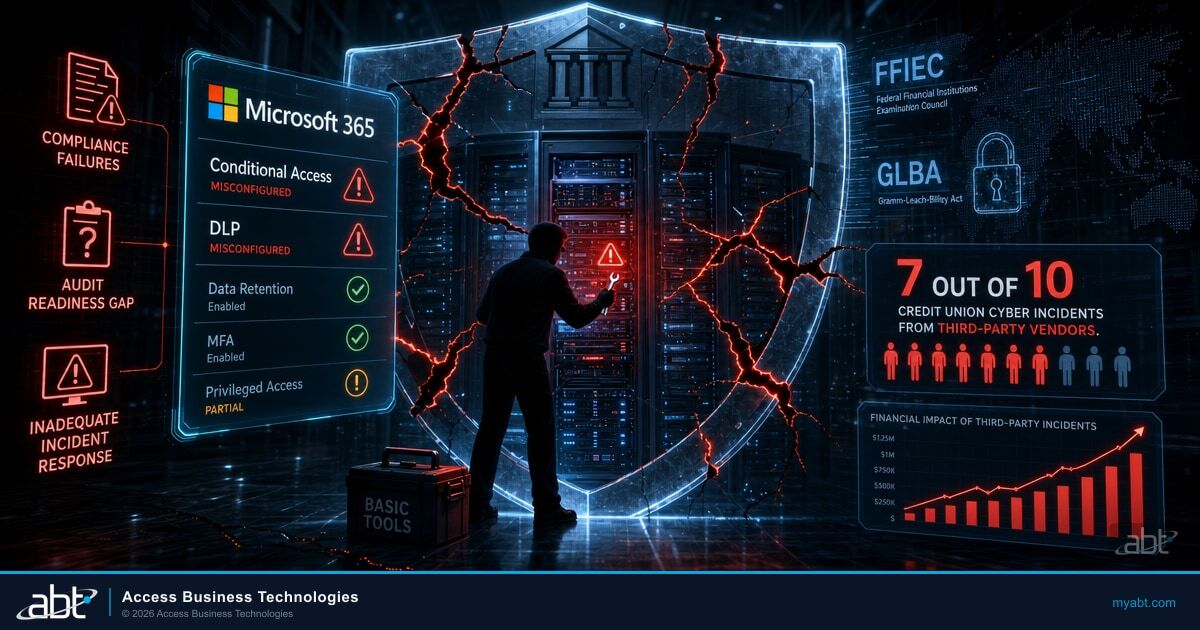
In this article: The Problem With Generic MSPs in Financial Services Five Ways Generic MSPs Fail Financial Services Clients The Real Cost of the...

11 min read
In This Article What the Treasury AI Risk Framework Is (and Isn't) The Seven Risk Domains Explained Which Controls Matter Most for Banks and Credit...

10 min read
In This Article What Changed for Financial Institutions in 2026 How Microsoft 365 Maps to New Examination Standards Key Microsoft 365 Features for...
11 min read
In This Article What Is Shadow AI and Why Banking Is Ground Zero The Scale of the Problem: What the Data Shows Five Shadow AI Scenarios That Keep...
