Skip to the main content.

ABT Blog

Read about mortgage technology solutions topics

cybersecurity

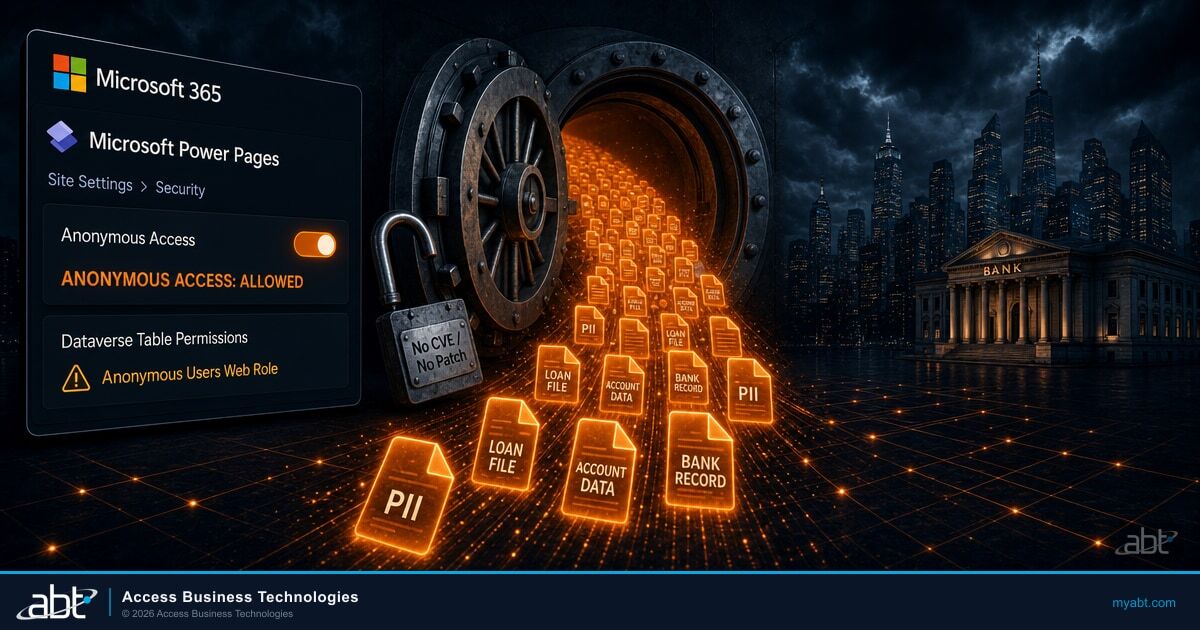
Microsoft Power Pages admin panel showing Anonymous Access set to Allowed, with customer records flowing out of an open vault

11 min read

Power Pages Misconfiguration: No CVE, No Patch

Two financial regulators flagged a Microsoft Power Pages setting that exposes Dataverse records. No CVE, no patch, and your scanner will not see it.
Read More
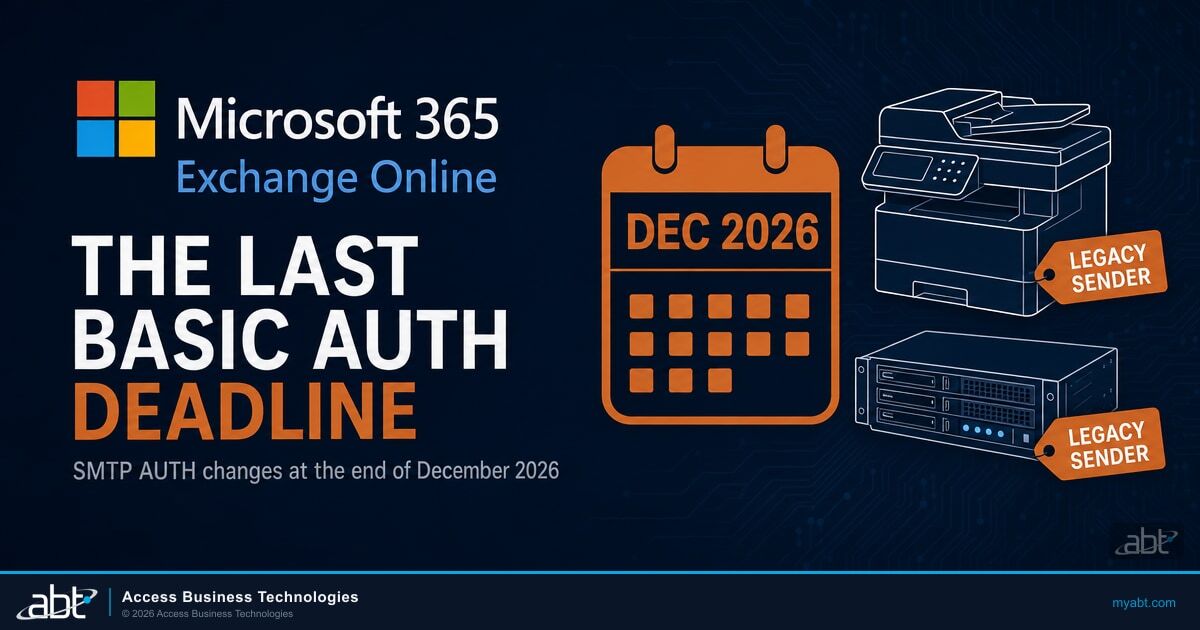
Microsoft 365 Exchange Online SMTP AUTH basic authentication deadline, December 2026, with legacy sender devices

13 min read

The Last Basic Authentication Deadline: SMTP AUTH Changes in December 2026

In This Article What actually changes at the end of December 2026 What in your institution still sends mail this way How to find every dependency...
Read More
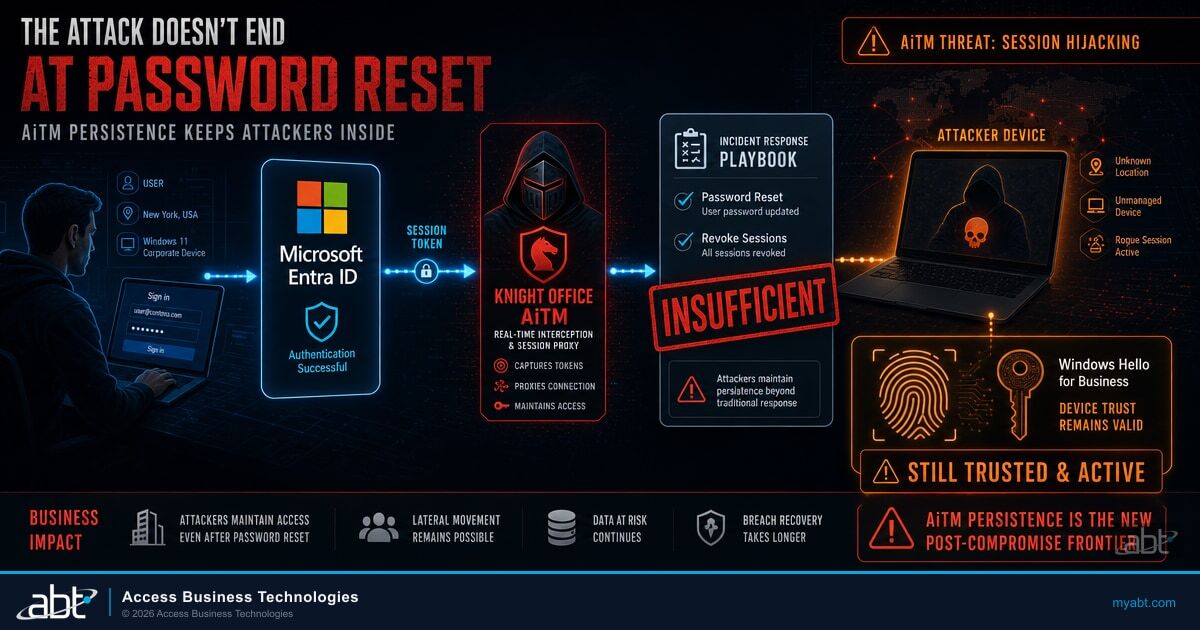
Microsoft 365 adversary in the middle attack chain ending in a registered Microsoft Entra ID device and an enrolled Windows Hello for Business credential

11 min read

Knight Office AiTM Kit: Persistence Past Password Reset

In This Article What Huntress found How this differs from the August Windows Hello research The step that survives your incident response Whether...
Read More
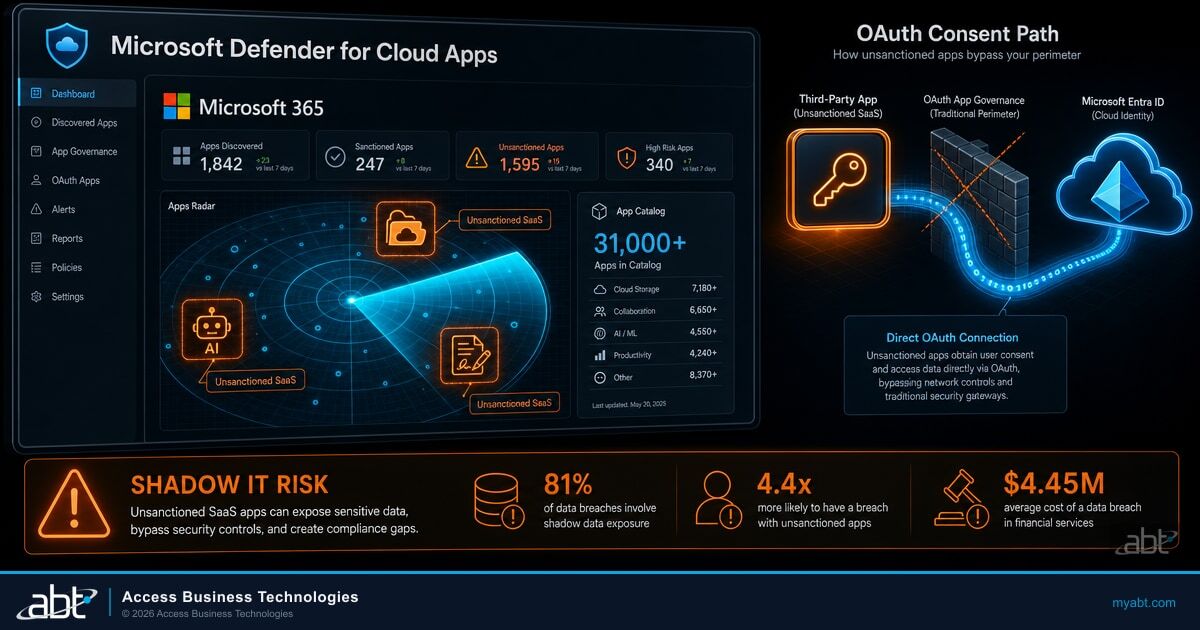
Shadow IT discovery dashboard showing sanctioned and unsanctioned cloud apps for a financial institution, with Microsoft 365 branding

15 min read

Shadow IT in Financial Institutions: Find It, Govern It

Your staff already told you which tools they need. They just did not ask first. How to find unsanctioned apps in a Microsoft 365 tenant with Defender...
Read More
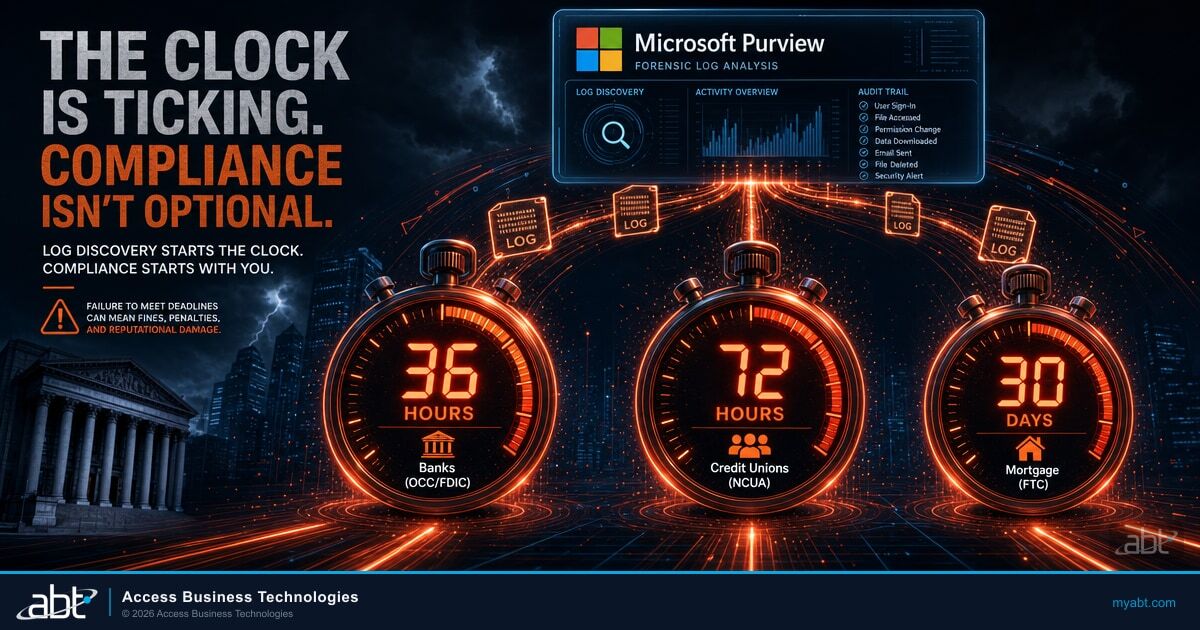
Cyber incident reporting deadlines for financial institutions, showing the 36 hour, 72 hour and 30 day regulatory clocks

12 min read

The 36-Hour, 72-Hour, and 30-Day Incident Reporting Clocks

Three federal rules, three deadlines, and three different definitions of the moment the clock starts. What triggers each one, and what Microsoft 365...
Read More
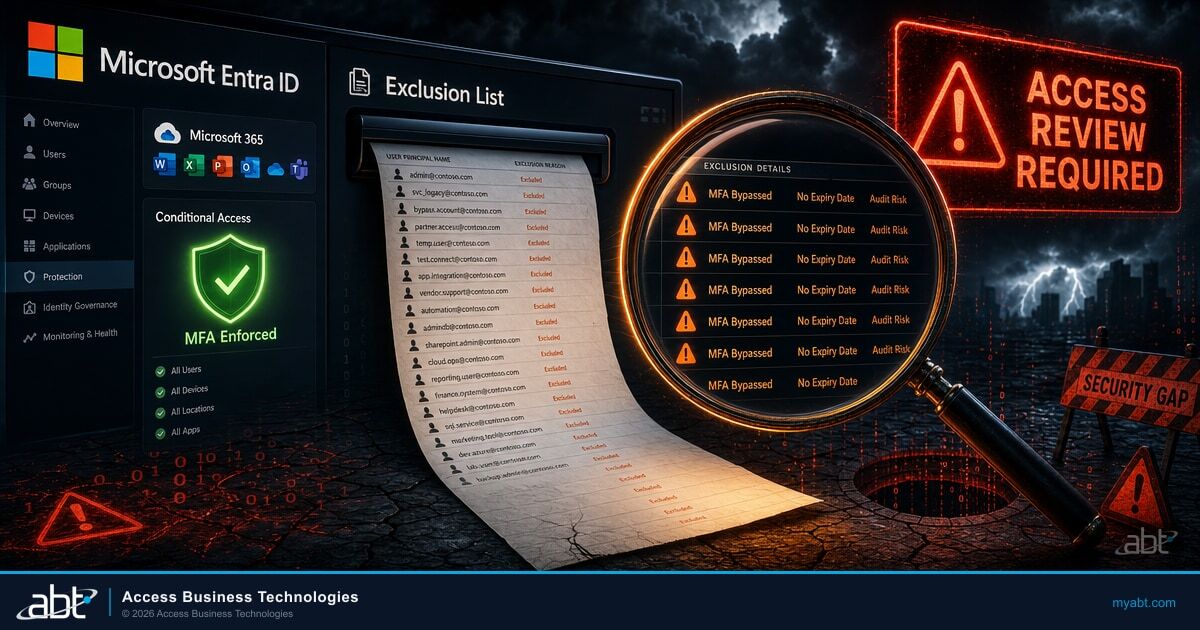
Microsoft Entra ID Conditional Access exclusion list review for financial institutions

12 min read

Conditional Access Exclusions: The List Nobody Reviews

Every institution grants Conditional Access exceptions. Microsoft documents how those lists grow, names access reviews as the compensating control,...
Read More
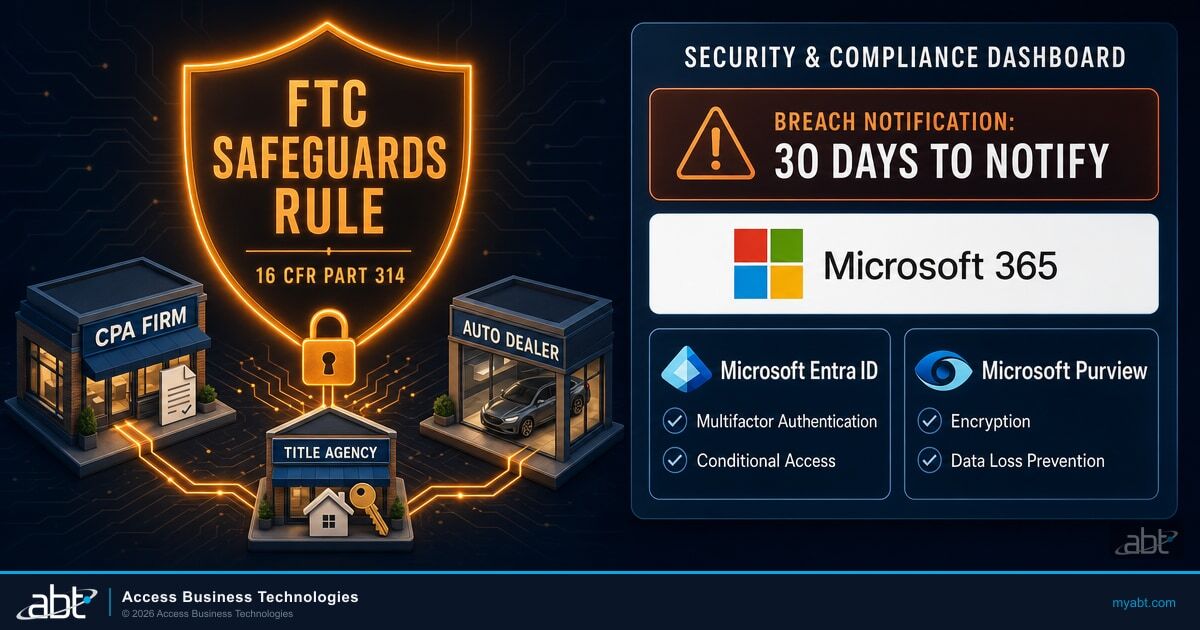
FTC Safeguards Rule shield covering a CPA firm, title agency, and auto dealer, with a Microsoft 365 security dashboard

9 min read

You Might Be Running a Financial Institution. The FTC Thinks So.

In This Article The Label You Did Not Choose Who Is Covered? The List Is Longer Than You Think What the Safeguards Rule Actually Requires What...
Read More
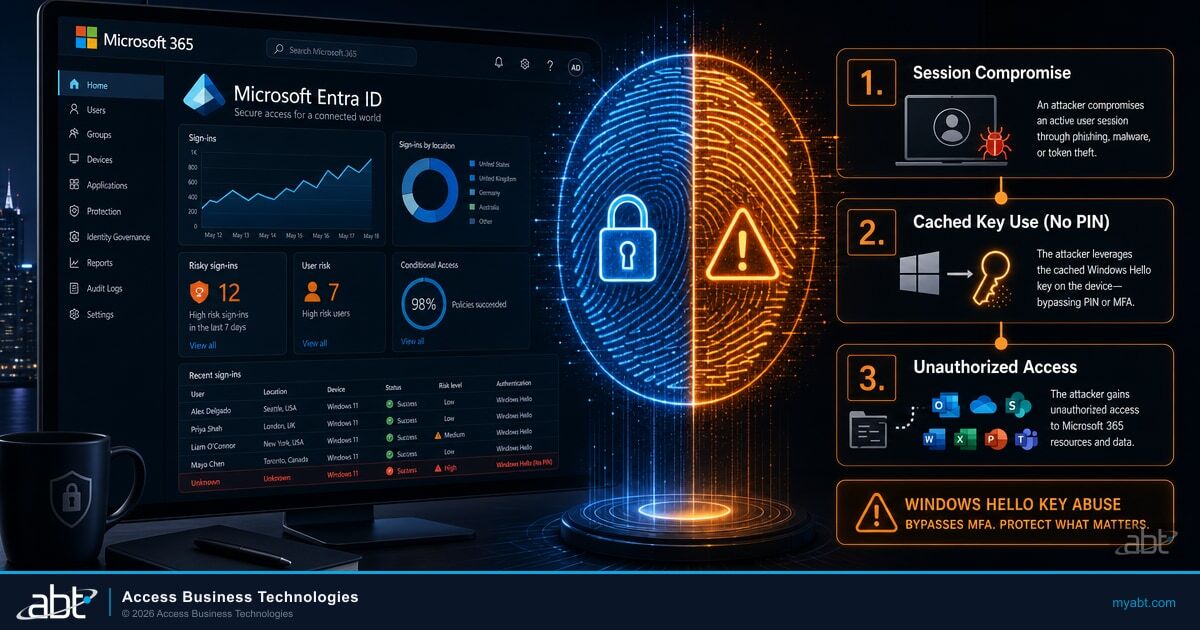
Windows Hello for Business key abuse and Microsoft Entra ID device registration

15 min read

Windows Hello for Business Key Abuse: What Financial Institutions Need to Verify

Malware already running in a signed-in Windows session can use that user's Windows Hello for Business key to authenticate to Microsoft Entra ID, with...
Read More
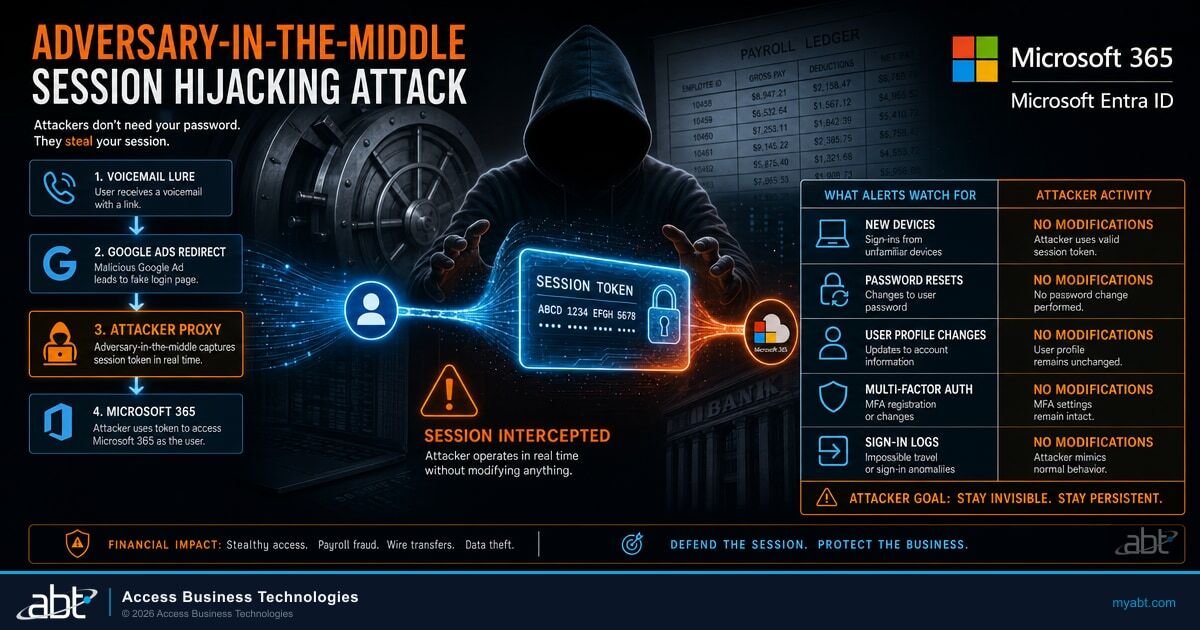
Dark editorial illustration of a hijacked Microsoft 365 session quietly reading payroll and finance mail while security alerts stay silent

13 min read

Payroll Pirates: The Microsoft 365 Attack Your Alerts Miss

A Microsoft 365 session-hijacking campaign is reading payroll and finance mail while deliberately avoiding the account-modification signals most...

Read More
Microsoft Entra ID legacy risk policies deactivated with an October 1 2026 deadline, replaced by Conditional Access protecting bank accounts

14 min read

Entra Risk Policies Retire Oct 1, 2026: What Banks Must Do

In This Article What actually changes on October 1 The self-service loop that goes away first The detections keep firing. No risk policy acts on...

Read More