Skip to the main content.

ABT Blog

Read about mortgage technology solutions topics

Risk Management

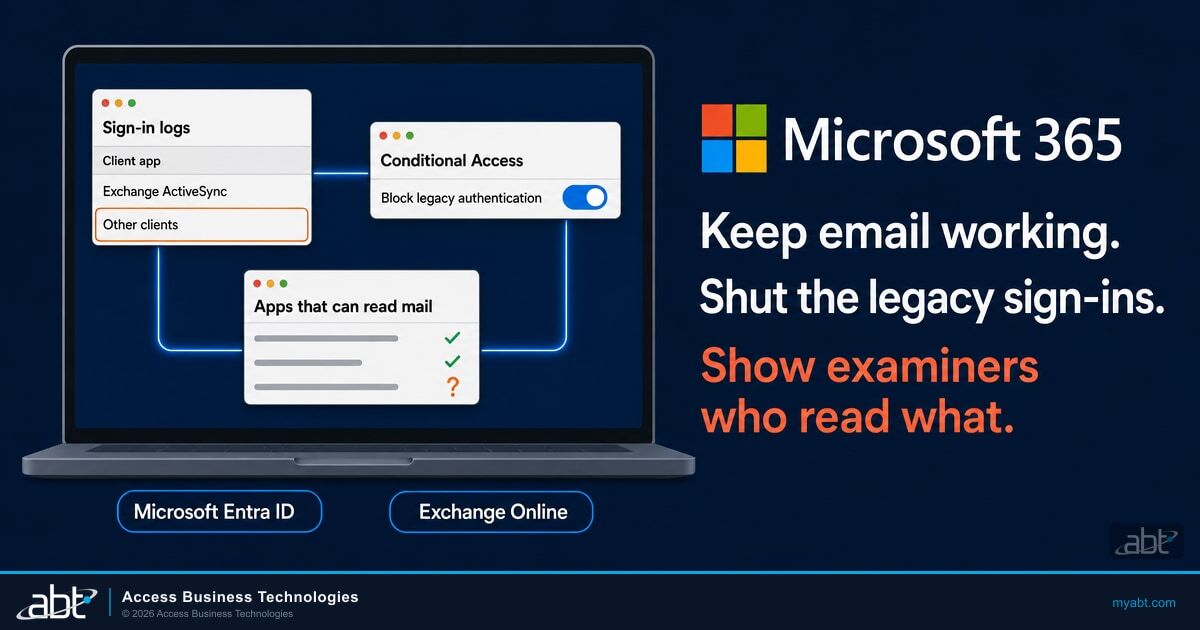
Microsoft 365 hero: Entra sign-in logs, a Conditional Access policy blocking legacy authentication, and apps that can read mail, headed Keep email working, Shut the legacy sign-ins, Show examiners who read what

12 min read

Flax Typhoon and Microsoft 365: What Banks, Credit Unions, and Lenders Should Check

In This Article What the October 8 Flax Typhoon advisory says Three tools aimed at Microsoft 365 mail Block the sign-ins a password spray depends on...
Read More
Microsoft 365 cybersecurity tabletop exercise for financial institutions: three inject cards, a laptop checklist, and a wall clock beside the lines Rehearse the first hour, Know who acts, Document every decision

12 min read

Cybersecurity Tabletop Exercise: Rehearse the First Hour of a Microsoft 365 Incident

In This Article What a cybersecurity tabletop exercise is Who belongs in the room Three Microsoft 365 scenarios to rehearse The notice clocks your...
Read More
Microsoft 365 illustration: a laptop shows a Please review and sign email, a Windows prompt asking to allow an app to make changes, and an Approved remote tools list, with Microsoft Intune and Microsoft Defender labels

11 min read

RMM Phishing: What Banks, Credit Unions, and Lenders Should Block

In This Article What Microsoft found in the RMM phishing campaigns Why signed remote tools slip through The administrator prompt decided the outcome...
Read More
Laptop showing three attack routes from the 2026 Microsoft Digital Defense Report: a Verify you are human prompt telling the user to press Win + R and paste, a Microsoft Teams call from an external caller, and an Outlook email asking Do you have a moment, beside the Microsoft 365 logo and the headline Keep staff working, Catch the stolen session, Report it to the board.

13 min read

Microsoft Digital Defense Report 2026: What Banks, Credit Unions, and Lenders Should Do First

In This Article Inside the Microsoft Digital Defense Report 2026 Attackers start with people and sign-ins Phishing now steals the session ClickFix...
Read More
Microsoft Azure illustration: an app identity passes a checkpoint to locked Storage, Key Vault, SQL Database and Backup vault tiles, with the headline Workloads keep running, Every app identity scoped, Recovery locked in

13 min read

Azure Service Principal Security: What Storm-3168 Deleted, and What Held

In This Article What Storm-3168 did inside one Azure tenant Why an Azure service principal is worth stealing What held, and why the attacker's roles...
Read More
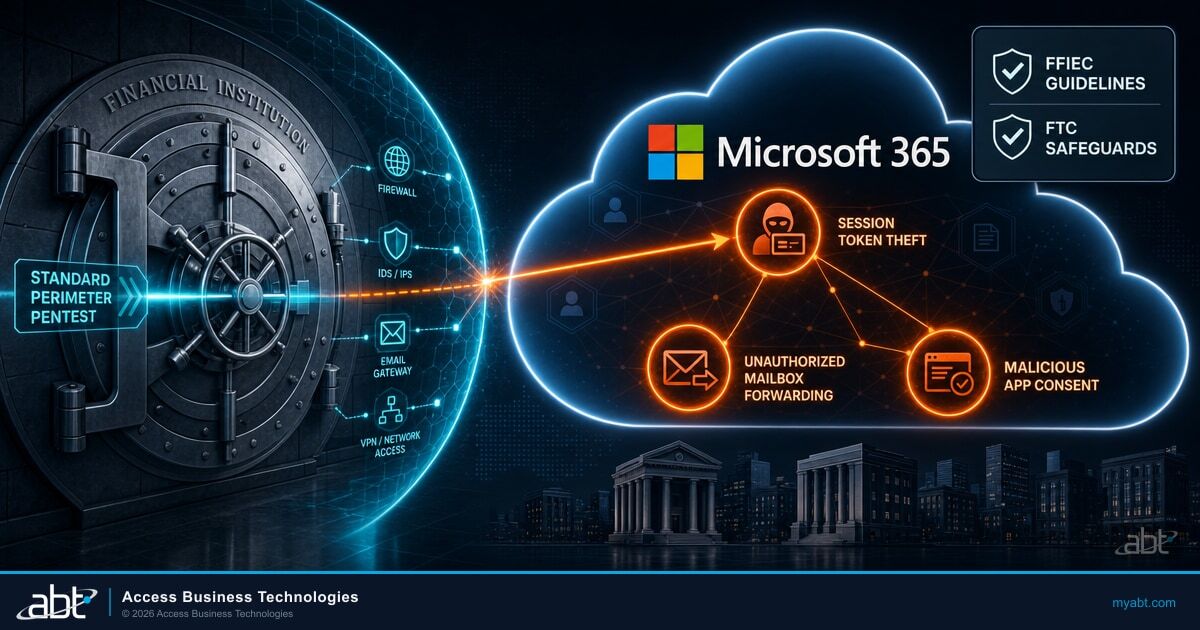
A standard perimeter penetration test stops at the network edge while session token theft, mailbox forwarding and malicious app consent happen inside the Microsoft 365 tenant

14 min read

Microsoft 365 Penetration Testing for Financial Institutions

In This Article What a penetration test is, in your regulator's words What your regulator actually requires What Microsoft permits you to test The...
Read More
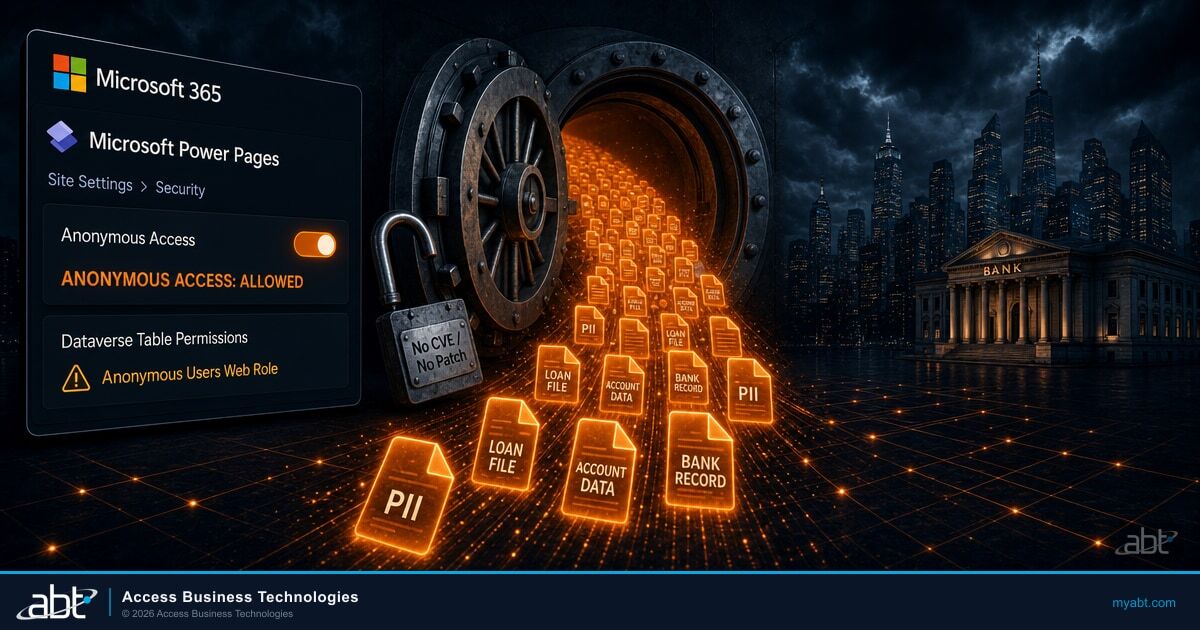
Microsoft Power Pages admin panel showing Anonymous Access set to Allowed, with customer records flowing out of an open vault

11 min read

Power Pages Misconfiguration: No CVE, No Patch

Two financial regulators flagged a Microsoft Power Pages setting that exposes Dataverse records. No CVE, no patch, and your scanner will not see it.
Read More
Two office buildings linked by Microsoft Entra cross-tenant synchronization and a multitenant organization, with the headline Keep the producers working, Link the tenants, Decide the end state later, and the Microsoft 365 logo

14 min read

Buying a Mortgage Company? Link the Microsoft 365 Tenants Before You Merge Them

In This Article The producers are the asset, and the cutover is the risk to the asset Three answers to "what happens to their tenant?" How the link...
Read More
An open manila vendor file folder on a desk holding printed audit reports, with a card bearing the Microsoft 365 logo resting on top and a tab labeled VENDOR FILE

17 min read

Vendor Due Diligence on Microsoft 365: What Goes in the File

In This Article The Questionnaire That Comes Back Empty The Passage That Answers This Step One: Document the Limitation Step Two: Obtain Alternative...
Read More
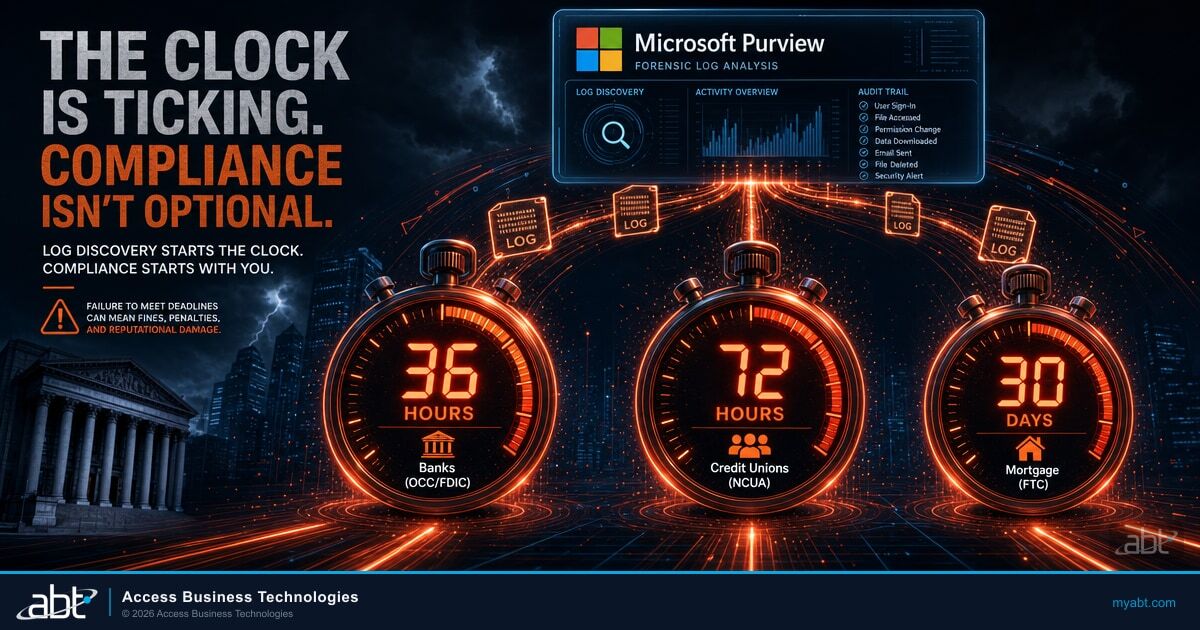
Cyber incident reporting deadlines for financial institutions, showing the 36 hour, 72 hour and 30 day regulatory clocks

12 min read

The 36-Hour, 72-Hour, and 30-Day Incident Reporting Clocks

Three federal rules, three deadlines, and three different definitions of the moment the clock starts. What triggers each one, and what Microsoft 365...

Read More