
In This Article
The Microsoft 365 outage is over. The phishing built on it kept arriving after service came back, and it quotes the real incident number.
Friday morning, a loan processor whose Outlook went dark on Thursday opens a message headed "Action required: (4) messages held after the outage." It names Exchange Online incident EX1550543, the same number her IT team mentioned, and says the held mail will be deleted within 24 hours unless she presses RESTORE MESSAGES.
Every detail she can check from her desk looks right. Microsoft never sent it, and Microsoft Threat Intelligence describes the campaign behind it as "consistent with credential phishing."
Late on Friday, November 13, Pacific time, Microsoft Threat Intelligence warned publicly that attackers were using the November 12 Microsoft 365 outage as a phishing lure. The warning went out 23 minutes after Microsoft 365 Status posted that service was restored "to the remaining impacted customers and regions."
This guide is for IT and security leaders at credit unions, banks, and mortgage companies running Microsoft 365. ABT is a Tier-1 Microsoft Cloud Solution Provider that has served 750+ financial institutions since 1999. Through Guardian MxDR, ABT monitors Defender alerts, sign-in anomalies, and configuration drift for financial institutions, which is where a campaign like this one shows up.
The short version: hunt for the lure this month, while your logs still hold it. Microsoft's own instructions for that hunt use tools from Defender for Office 365 Plan 2, which Microsoft 365 Business Premium alone doesn't include. Then write down what your institution did during the outage, because that record is what an examiner will ask to see.
What Microsoft warned about
"Microsoft Threat Intelligence observed an active phishing campaign exploiting the Microsoft 365 service disruption on November 12. The messages impersonate Microsoft 365 service health notifications and reference the legitimate Exchange Online incident EX1550543."
Microsoft's post adds the detail a mail administrator needs. "Some of the phishing emails Microsoft detected on November 13 falsely claim that messages were held during the outage and will be deleted within 24 hours unless recipients click to restore them." Subjects follow the pattern "Outage - [six-character code]." Sender display names start with an organization-specific prefix and end in "Outage Notification" or "Service Health," so the name in the From line can look like it came from your own IT team.
The campaign uses three sender domains, moments-notice[.]com, planetmaison[.]com and newbooker[.]com, and Microsoft says recipient-specific SendGrid click-tracking links redirect to reallifeaccounting[.]com, including the path /themelist0.html. SendGrid is a legitimate bulk email service, which helps the links look ordinary to a filter and to a reader.
Microsoft is careful about what it knows. "The activity is consistent with credential phishing, although credential collection and malware delivery have not been confirmed." It also says, "Similar messages targeted organizations across multiple US sectors."
Microsoft names no sector. Financial institutions run on the same Exchange Online service that failed, received the same real outage notices, and have staff who spent Thursday waiting for mail to come back.
Search for these indicators, and expect new ones
The domains and subject pattern above are what Microsoft published on November 14 (UTC). Senders and landing pages rotate. Use them to search your mail logs now, and rely on the controls that hold when the details change: Safe Links, user reporting, and multifactor authentication (MFA) that resists phishing.
Why Microsoft 365 outage phishing works
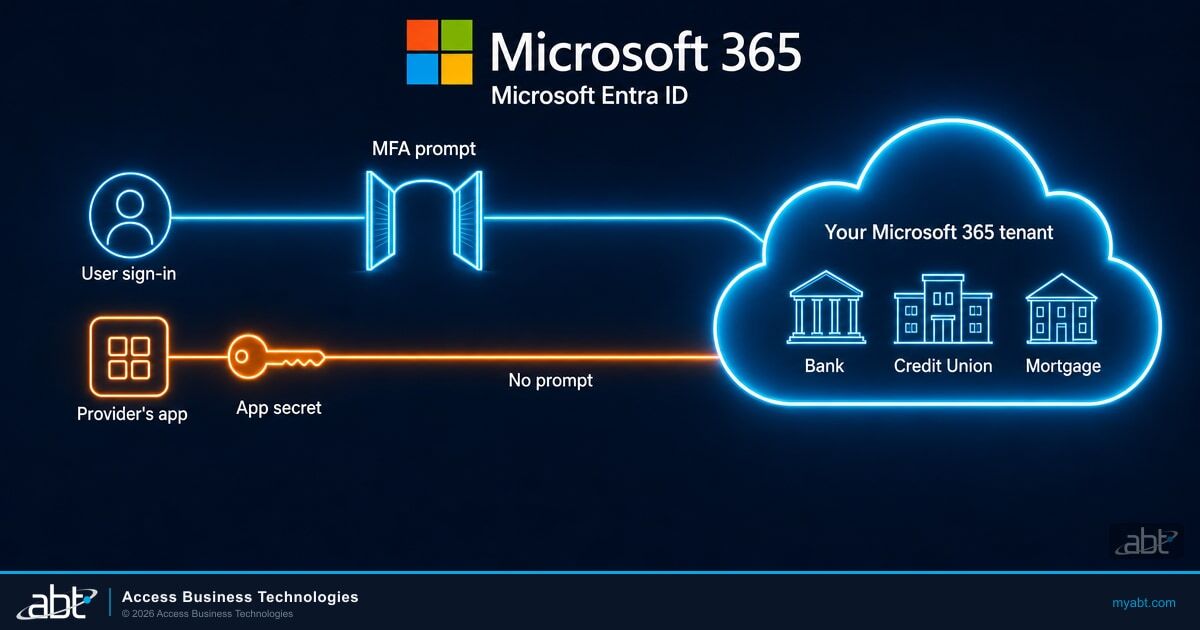
Real service health notices arrive by email. Microsoft's service health guide shows administrators how to sign up for "email notifications of new incidents that affect your tenant." Staff who heard about the outage from IT on Thursday were primed to expect exactly this message, from exactly this source, about exactly this incident.
The lure's central claim is false. During the incident, Microsoft's service health update for EX1550543 said it was "extending the email timeout window to 48 hours to help protect delayed messages while service recovery continues." Microsoft's fix for delayed mail was to hold it longer, and nothing about restoring it requires a user to click anything.
That makes the request itself the tell. Real service health updates are written for administrators and live in the Microsoft 365 admin center, so a message asking a staff member to restore mail from a button is the lure.
| What to look at | A real Microsoft 365 service health update | The outage lure Microsoft described |
|---|---|---|
| Where the full update lives | Health > Service health in the Microsoft 365 admin center | A button in the email |
| What it asks a user to do | Updates are written for administrators | "RESTORE MESSAGES" before a 24-hour deadline |
| What it says about delayed mail | Timeout extended to 48 hours "to help protect delayed messages" | Held messages "will be deleted within 24 hours unless released" |
| Sender | Your tenant's service health notification settings | Display name ending in "Outage Notification" or "Service Health," sent from unrelated domains |
| Where to confirm when the admin center is down | status.cloud.microsoft and @MSFT365Status | The link in the message |
From that table, the staff message is one sentence long: IT will never ask you to restore mail from a link, and anything about an outage gets checked with IT first. Send it through a channel other than email, such as a Teams post, a text or the intranet, because email was the channel that failed.

What happened on November 12
Microsoft's service health record for EX1550543 and MO1550821 gives the outage a start of 4:20 PM UTC on Thursday, November 12 (11:20 AM ET). The recorded end is 4:10 PM UTC on Friday, November 13 (11:10 AM ET), about 24 hours later. Microsoft finished restoring the remaining customers and regions at 06:09 UTC on Saturday, November 14. Press reports put the outage anywhere from about 10 hours to more than 24, depending on when and where they measured; Microsoft's record is the figure to use in your own incident file.
Microsoft opens EX1550543, first titled "Potential issues accessing mailboxes via one or more connection methods."
MO1550821 widens the incident to Teams, SharePoint Online, Copilot and Defender XDR.
Microsoft's recorded end time, with queued mail still draining afterward.
Service restored to the remaining customers and regions.
Microsoft Threat Intelligence warns of the outage-themed phishing campaign.
On cause, Microsoft's final service health entry is plain: "This was a technical issue not related to cyber or AI / agents."
The preliminary post-incident review, released in the admin center on November 16 UTC, names three factors. A fix built for the networking gateway servers that front many Microsoft 365 services carried a latent defect, and the review, as summarized by Microsoft executive vice president Charles Lamanna, says "lock contention inside an internal process" made servers unresponsive under certain loads. About fifteen hours earlier, Teams had failed over onto the same gateway that supports Exchange Online. And "nearly 14% of server capacity for the networking gateway was out of service due to an unrelated issue from the previous day."
Two lines from the review answer questions your board may ask. Exchange Online took the longest because, unlike Teams, OneDrive and SharePoint, it can't fail away from that gateway. And the defect is Microsoft's to fix: "neither the underlying defect nor the fix applies to broader Windows deployments." Your own Windows servers need nothing from this incident.
Microsoft says the final post-incident review will follow later this week; read it in the admin center under MO1550821 and keep a copy with your incident record.
Run the hunt Microsoft describes
Microsoft's post names the tools: "Security teams can use Microsoft Defender for Office 365 Threat Explorer and Microsoft Defender XDR advanced hunting (EmailEvents, EmailUrlInfo, and UrlClickEvents) to identify suspicious messages, examine embedded URLs, and investigate user clicks." Here is that hunt as a short list, in the order we run it.
In Threat Explorer, search from November 12 onward for the three sender domains and for subjects that start with "Outage -". Plan 1 tenants have Real-time detections instead, which shows only messages Defender flagged as malware or phishing. Also run a message trace in the Exchange admin center for each sender domain (it accepts a wildcard sender in the form *@domain) and for subjects that start with "Outage -".
The UrlClickEvents table "contains information about Safe Links clicks from email messages, Microsoft Teams, and Office 365 apps." Any user who clicked through to the landing domain is the start of an investigation.
For each user who clicked, review Microsoft Entra sign-in logs from the click onward for unfamiliar locations, new devices or new MFA methods. If anything looks wrong, revoke sessions and reset the password before you finish the paperwork.
Remove delivered copies from mailboxes: Plan 2 tenants act from Threat Explorer, and Plan 1 tenants can use a Microsoft Purview content search and purge. Then block the sender domains in the Tenant Allow/Block List.
Microsoft says Safe Links "provides time-of-click protection against malicious URLs when properly configured." Confirm every user falls under a Safe Links policy and review your "Do not rewrite the following URLs" list, since entries there "aren't scanned or wrapped by Safe Links during mail flow."
Turn on Outlook's built-in Report button and send reports to a reporting mailbox. Microsoft's guidance reads "Identify the reporting mailbox as a SecOps mailbox," which keeps reported phishing from being filtered before it reaches your team.
For teams that hunt in Defender XDR, this query is a starting point. It looks for the messages by sender domain or subject, then joins the clicks:
let lure = EmailEvents
| where Timestamp > datetime(2026-11-12)
| where SenderFromDomain in ("moments-notice.com", "planetmaison.com", "newbooker.com")
    or Subject startswith "Outage - "
| project NetworkMessageId, Timestamp, RecipientEmailAddress, SenderFromDomain, Subject, DeliveryAction;
lure
| join kind=leftouter (UrlClickEvents | project NetworkMessageId, ClickTime = Timestamp, Url, AccountUpn, ActionType, IsClickedThrough) on NetworkMessageId
Add EmailUrlInfo, joined on NetworkMessageId, to see which URLs each message carried. Then mind the clock. Advanced hunting explores "up to 30 days of raw Defender data," so messages Microsoft detected on November 13 drop out of the default window around December 13. Export what you find before then.
Now the licensing catch. Microsoft Learn says "Threat Explorer is available in Defender for Office 365 Plan 2" and "Real-time detections is available in Defender for Office 365 Plan 1." Microsoft's Defender for Office 365 overview places Plan 1 in Microsoft 365 Business Premium and lists advanced hunting among the Plan 2 capabilities. Microsoft also gives a quick test: if your Defender portal shows Email & collaboration > Real-time detections, you're on Plan 1.
On Business Premium alone, you can find these messages with message trace and Real-time detections, pull them with a Microsoft Purview content search and purge, and protect clicks with Safe Links. Threat Explorer and advanced hunting, the tools Microsoft named for this hunt, come with Defender for Office 365 Plan 2.
Microsoft offers Plan 2 to Business Premium customers through Microsoft Defender Suite for Microsoft 365 Business Premium, which also adds Microsoft Entra ID P2 and Defender for Endpoint Plan 2. Plan it for every user, because a lure like this one goes to everyone. ABT is a Tier-1 Microsoft Cloud Solution Provider, so the Defender Suite goes on your ABT quote like the rest of your Microsoft licensing, at Microsoft price. Our guide to the Defender for Office 365 anti-phishing configuration examiners expect covers the policy settings in detail.
Step three, checking every clicker's sign-ins and cutting off a stolen session, is where a two-person IT team runs out of hours. It is the step Guardian MxDR is built around.
Guardian Contain adds "pre-authorized automated containment that revokes a compromised session in seconds at any hour." On Guardian Respond, when MxDR identifies a threat, ABT engineers "assess severity, trace the attack path, and determine scope" and handle account isolation and password reset during business hours. Guardian Resolve puts "a human on the incident at any hour."

Your security tools were in the outage too
The outage reached past mailboxes. Microsoft's final list of affected features for MO1550821 says "Users may be unable to load Microsoft Defender portal pages or solution tabs." It says Purview "Audit searches" and "eDiscovery tasks such as search and export" may have been affected, and that Intune device compliance "may have been intermittently impacted." Admins "may be unable to load some admin center pages."
Read that list as a security leader. The attackers chose this outage as their lure. During it, three of your tools were degraded: the portal to hunt for their mail, the audit search to trace a sign-in, and the admin center to confirm the incident. Microsoft's own fallback for that last one was status.cloud.microsoft "if the admin center is not available to you."
- Write down where your team checks Microsoft 365 status when the admin center won't load, and who gets the service health emails. Microsoft allows up to two addresses per admin for those notifications.
- Decide how staff hear from IT when email is down: a Teams channel, a text list or the intranet.
- Keep a record of what you couldn't see and when. If a sign-in alert went unread for six hours because the portal wouldn't load, that gap belongs in your incident file.
- Rehearse it. Our Microsoft 365 tabletop exercise guide has a first-hour drill you can adapt to a provider outage.
What examiners will ask
The standing guidance already covers this outage, and it was written for this kind of event: a widely used provider failing all at once.
"A critical failure at a widely used third-party service provider could have large-scale consequences."
The same section warns that a provider "can be a single point of failure if management has not considered alternative providers or other contingency plans." It lists "Alternative resource options (e.g., personnel and systems) for when primary services cannot be delivered" among the things management should consider. The NCUA is an FFIEC member agency, so the booklet's principles reach credit unions as well as banks. For banks, the 2023 interagency guidance on third-party relationships adds: "It is important to assess options to employ if the third party's ability to perform the activity is impaired."
What the booklet asks for is a plan you can show: how you communicated when email failed, how loan closings and member service kept moving, and how you handled the phishing that followed. Our FFIEC business continuity guide covers the recovery side, and our backup tenant guide covers keeping a copy of your mail outside the tenant.
Then there's notification. The 2021 computer-security incident notification rule requires a bank to notify its primary federal regulator no later than 36 hours after determining that a notification incident occurred. Its definition of an incident covers events "from whatever cause." Federally insured credit unions have a 72-hour window under the NCUA's rule, explained in Letter to Credit Unions 23-CU-07.
Whether this outage, or a click on the lure, met either threshold is a call for your compliance officer and counsel. Make the call in writing and keep it in the file.
How ABT and Guardian MxDR help
Defender generates the signals, but something has to act on them, including at 2 in the morning when a two-person IT team is asleep. That is why M365 Guardian "puts automated containment on duty around the clock." Outage-themed phishing tests that directly, because it lands when the IT team is already busy with the outage.
Guardian MxDR covers email threats: "Phishing campaigns, business email compromise, malware attachments, and impersonation attempts monitored through Defender for Office 365." Its detection step includes cross-tenant threat intelligence. "Every alert feeds into a single monitoring pipeline managed by ABT engineers who understand your environment."
When it identifies a threat, "automation contains it in seconds at any hour, and ABT engineers follow a structured response process: during business hours on Guardian Respond, and at any hour on Guardian Resolve." Guardian Respond also produces "a written incident timeline suitable for an examiner or an insurer," which is the record the previous section asks you to keep.
Our Guardian page states the licensing point plainly: Business Premium includes "Microsoft Defender for Office 365 Plan 1," and "examiners increasingly expect risk-based Conditional Access (Microsoft Entra ID P2) and around-the-clock monitoring that Business Premium alone does not include." This campaign adds a second reason: the hunt Microsoft describes runs on Plan 2. "Your Microsoft licensing is quoted separately, at Microsoft price."
The free ABT Security Assessment reviews "SPF, DKIM, and DMARC configuration. Anti-phishing policies. Defender for Office 365 settings. Safe Links and Safe Attachments status." That's the "properly configured" half of Microsoft's advice. It's a read-only review of how your tenant is set up, and it ends with a prioritized hardening roadmap. The hunt for who clicked is the checklist above, and on Guardian Respond, ABT engineers take it on during business hours.
"If you have Defender but nothing acting on it, you have detection without response."
Serving 750+ financial institutions since 1999
Check Safe Links today, then let Guardian MxDR act on the next lure
ABT's free Security Assessment is a read-only review of your anti-phishing policies, Safe Links and Safe Attachments status, Defender for Office 365 settings, and SPF, DKIM and DMARC, ending in a prioritized hardening roadmap. Guardian MxDR then acts on what Defender finds, with automation that contains threats in seconds at any hour.
Frequently Asked Questions
Microsoft Threat Intelligence warned on November 14, 2026 that attackers were sending fake Microsoft 365 service health notices that cite the real Exchange Online incident EX1550543. Some claim mail held during the outage will be deleted within 24 hours unless the recipient clicks to restore it. Microsoft says the activity is consistent with credential phishing.
Microsoft's final service health status says it was a technical issue unrelated to a cyberattack. The preliminary post-incident review traces it to a latent defect in a fix for Microsoft 365 networking gateway servers, a Teams failover onto the same gateway, and reduced gateway capacity. Together they left more than 80% of gateway servers unresponsive at the low point.
Microsoft's record gives a start of 4:20 PM UTC on November 12, 2026 and an end of 4:10 PM UTC on November 13, about 24 hours. Microsoft finished restoring the remaining customers and regions early on November 14 UTC. Press estimates ranged from about 10 hours to more than 24.
Join EmailEvents to UrlClickEvents on NetworkMessageId in Defender XDR advanced hunting, filtered to the sender domains Microsoft published. Advanced hunting keeps 30 days of data by default, so run it before mid-December. Defender for Office 365 Plan 1 tenants can find the messages with a message trace. On Guardian Respond, ABT security engineers investigate covered incidents during business hours.
Business Premium includes Defender for Office 365 Plan 1, which offers Real-time detections. Threat Explorer and advanced hunting come with Plan 2. Microsoft Defender Suite for Microsoft 365 Business Premium adds Plan 2 along with Entra ID P2 and Defender for Endpoint Plan 2.
Microsoft points administrators to status.cloud.microsoft and the @MSFT365Status account on X when the Microsoft 365 admin center is unavailable. Normally, read updates under Health, then Service health in the admin center, and never act on a link in an email that claims to be a service health notice.
Each rule has its own test. Banks notify their primary federal regulator as soon as possible, within 36 hours of determining a notification incident occurred. Federally insured credit unions notify the NCUA as soon as possible, within 72 hours of reasonably believing a reportable cyber incident occurred. Your compliance officer and counsel make the call; document the decision either way.